Shellshock - Pwnable.kr
Pwnable.kr Shellshock writeup: abusing the CVE-2014-6271 Bash environment-variable parsing bug to execute arbitrary commands and read the flag.
Pwnable.kr Shellshock writeup: abusing the CVE-2014-6271 Bash environment-variable parsing bug to execute arbitrary commands and read the flag.
Pwnable.kr Input writeup: feeding a program the right argv, environment variables, stdio pipes, file contents, TCP socket and UNIX socket to clear every stage.
A practical guide to ARP cache poisoning with Ettercap: running man-in-the-middle attacks on a LAN, sniffing traffic and applying Ettercap filters.
How to build a virtual network with QEMU using TAP interfaces, bridges and host routing, so you can experiment with networking and network attacks without physical hardware.
Pwnable.kr Random writeup: exploiting an unseeded call to rand() in C, whose predictable pseudo-random value lets us XOR our way to the expected 0xdeadbeef.
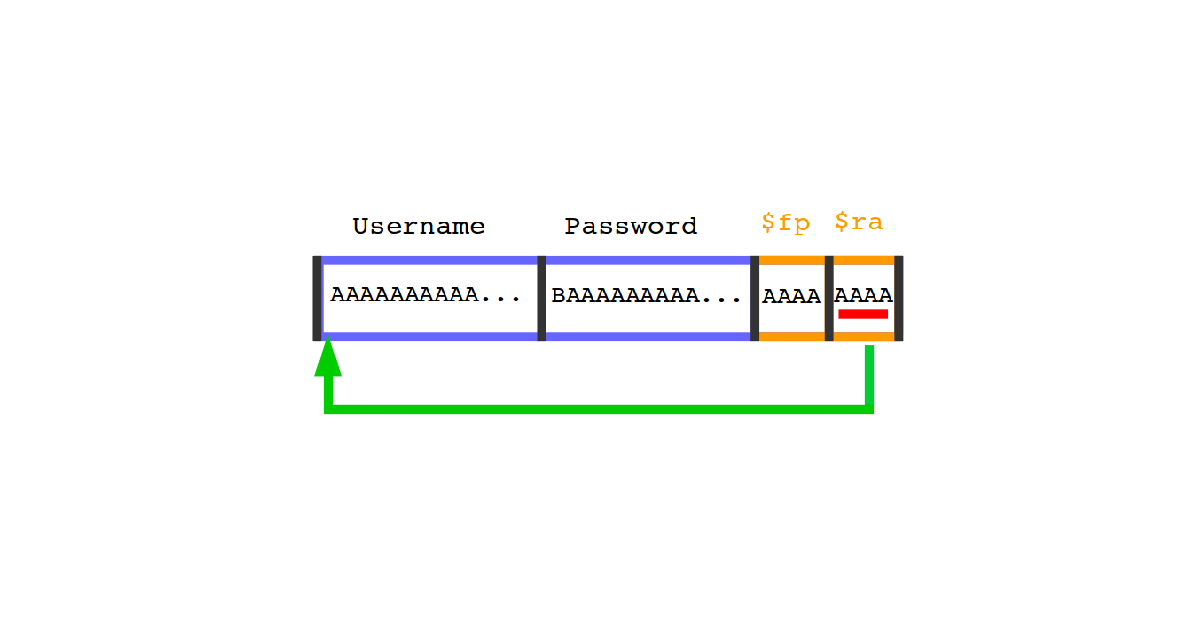
A hands-on introduction to stack buffer overflows on the MIPS architecture, and how its RISC calling convention and register-based returns change classic stack smashing.

Walkthrough of levels 0 to 16 of the Natas web security wargame on OverTheWire, covering source disclosure, path traversal, command injection, file inclusion and SQL injection.

Walkthrough of all seven levels of the Leviathan wargame on OverTheWire, covering basic Linux privilege escalation, file inspection, ltrace and setuid binary tricks.